Explained: FastAPI-based Tools Exposed to Authentication Bypass by Flaw in Starlette Framework
A flaw in the Starlette framework can let attackers bypass authentication on FastAPI-based tools, allowing unauthorized users to access AI services and sensitive data. The vulnerability can be exploited by specially crafted requests that manipulate authentication handling.
Key takeaways
- The root cause is a Starlette handling issue that affects FastAPI because FastAPI relies on Starlette for request and authentication handling.
- Consequences for affected AI tools include data theft, data manipulation, and the possibility of attackers gaining full control of systems, which harms operations and customer trust.
- Several real incidents were reported: a fintech startup had user financial data exposed and a healthcare application exposed patient records, leading to regulatory and reputational problems.
- Developers should identify affected Starlette and FastAPI versions, apply patches promptly, and run regular security audits and penetration tests.
- Recommended defenses include keeping dependencies up to date and adding multi-factor authentication to reduce the risk of unauthorized access.
Explained: FastAPI-based Tools Exposed to Authentication Bypass by Flaw in Starlette Framework
Developers using fastapi-based tools exposed authentication vulnerabilities due to a flaw in the Starlette framework are facing serious security challenges. The issue has left many AI tools at risk, leading to potential unauthorized access and data breaches. This article delves into the implications of this vulnerability, providing insights into the affected systems and offering strategies for mitigating such risks. Understanding how this flaw operates and what developers can do to protect their applications is crucial for maintaining secure and reliable AI tools.
1. Understanding the FastAPI-Based Tools Exposed Authentication Vulnerability
The fastapi-based tools exposed authentication issue arises from a vulnerability within the Starlette framework, which FastAPI relies on. This flaw allows attackers to bypass authentication mechanisms, gaining unauthorized access to sensitive data. The problem is rooted in how Starlette handles certain authentication requests, inadvertently allowing malicious users to exploit weaknesses in the system.
- Practical point 1: The vulnerability can be triggered by specially crafted requests that manipulate authentication headers, bypassing normal security checks.
- Practical point 2: Developers need to be aware of the specific versions of Starlette and FastAPI that are affected and apply patches promptly.
- Practical point 3: Real-world applications have already reported breaches, emphasizing the need for immediate action.
For a comprehensive understanding of FastAPI's architecture, developers can visit ContentPod for more resources on secure development practices.
2. Implications of the Starlette Flaw on AI Tools
The implications of the fastapi-based tools exposed authentication flaw extend beyond simple unauthorized access. AI tools that rely on FastAPI for their API services can be severely compromised, leading to data theft, manipulation, and even complete system control by attackers. The repercussions for businesses using these tools are significant, affecting both operational integrity and customer trust.
Read more about similar challenges in AI and content security in our related blog post: Unlocking Success with Interview-Based Content Marketing SaaS.
3. How FastAPI Developers Can Address the Vulnerability
Developers must take a proactive approach to address the fastapi-based tools exposed authentication issue. By implementing robust security measures and keeping their software up to date, they can mitigate potential risks. Regular audits and vulnerability assessments are critical to ensure that applications remain secure.
An insightful discussion on the future of AI security can be found in our featured interview: AI and the Future of Content Marketing: A Dynamic Discussion.
4. Real-World Examples of the Flaw's Impact
Several companies have reported breaches due to the fastapi-based tools exposed authentication flaw. These incidents highlight the critical need for vigilance and prompt response to security alerts. By examining these cases, developers can learn valuable lessons and implement effective countermeasures.
- Example 1: A fintech startup experienced unauthorized access to user data, leading to a significant breach that compromised sensitive financial information.
- Example 2: A healthcare application faced a security incident where patient records were exposed, causing regulatory challenges and reputational damage.
For more strategies on protecting sensitive data, refer to our blog on future-proofing business technology: The Future Store Deloitte: Redefining Retail in 2026.
5. Best Practices for Securing FastAPI-Based Tools
To prevent future vulnerabilities, developers should adopt best practices for securing fastapi-based tools exposed authentication issues. These practices include regular software updates, implementing multi-factor authentication, and conducting thorough security testing.
- Best Practice 1: Keep all dependencies up to date, particularly those related to authentication and security.
- Best Practice 2: Utilize multi-factor authentication to add an extra layer of security for user access.
- Best Practice 3: Regularly conduct penetration testing to identify and patch vulnerabilities before they can be exploited.
Explore more about securing digital tools at ContentPod.
6. Avoiding Common Mistakes When Handling Authentication
Understanding common pitfalls in handling authentication can help developers avoid similar issues in the future. Mistakes such as neglecting to update libraries or ignoring security advisories significantly increase the risk of exploitation.
For further reading on authentication security, consider visiting this detailed article on recent security trends.
Conclusion: Making the Most of FastAPI-Based Tools Exposed Authentication
By understanding and addressing the fastapi-based tools exposed authentication flaw, developers can protect their AI applications from potential threats. Implementing best practices and staying informed about security developments are essential steps in maintaining robust defenses. For additional resources, ContentPod offers a variety of tools and insights into secure development practices.
Frequently Asked Questions
What is fastapi-based tools exposed authentication?
This term refers to vulnerabilities in FastAPI applications due to flaws in the underlying Starlette framework, which can lead to authentication bypass and unauthorized access.
How can developers protect their applications from this vulnerability?
Developers should apply patches, update dependencies regularly, and implement robust authentication mechanisms such as multi-factor authentication to mitigate risks.
What are the consequences of ignoring such vulnerabilities?
Ignoring these vulnerabilities can lead to data breaches, unauthorized access, and significant damage to an organization's reputation and financial standing.
References & Further Reading
- News Article on Starlette Vulnerability
- OpenAI's Security Best Practices
- Anthropic's AI Security Trends 2026
- NIST's Security Controls for Organizations
Share this post
You Might Also Like
Discover more content tailored to your interests
 Highly Relevant
Why anthropic model rivals fable on enterprise cost
Anthropic's model is being pitched as close enough in quality to a premium frontier model that cost-conscious enterprises may switch or diversify. The real test for buyers is whether the model delivers acceptable output on their highest-volume tasks while lowering total operating cost and governance overhead.
Read More Highly Relevant
How AI in sports marketing is changing broadcast ads
AI in sports marketing is enabling rights holders, networks, streaming platforms, and brands to sell more relevant inventory, adjust creative in real time, and tie ad performance to audience behavior across linear TV, streaming, social clips, and second-screen engagement. Those capabilities let teams coordinate campaigns across fragmented viewing paths and react to moment-level attention during live games.
Read More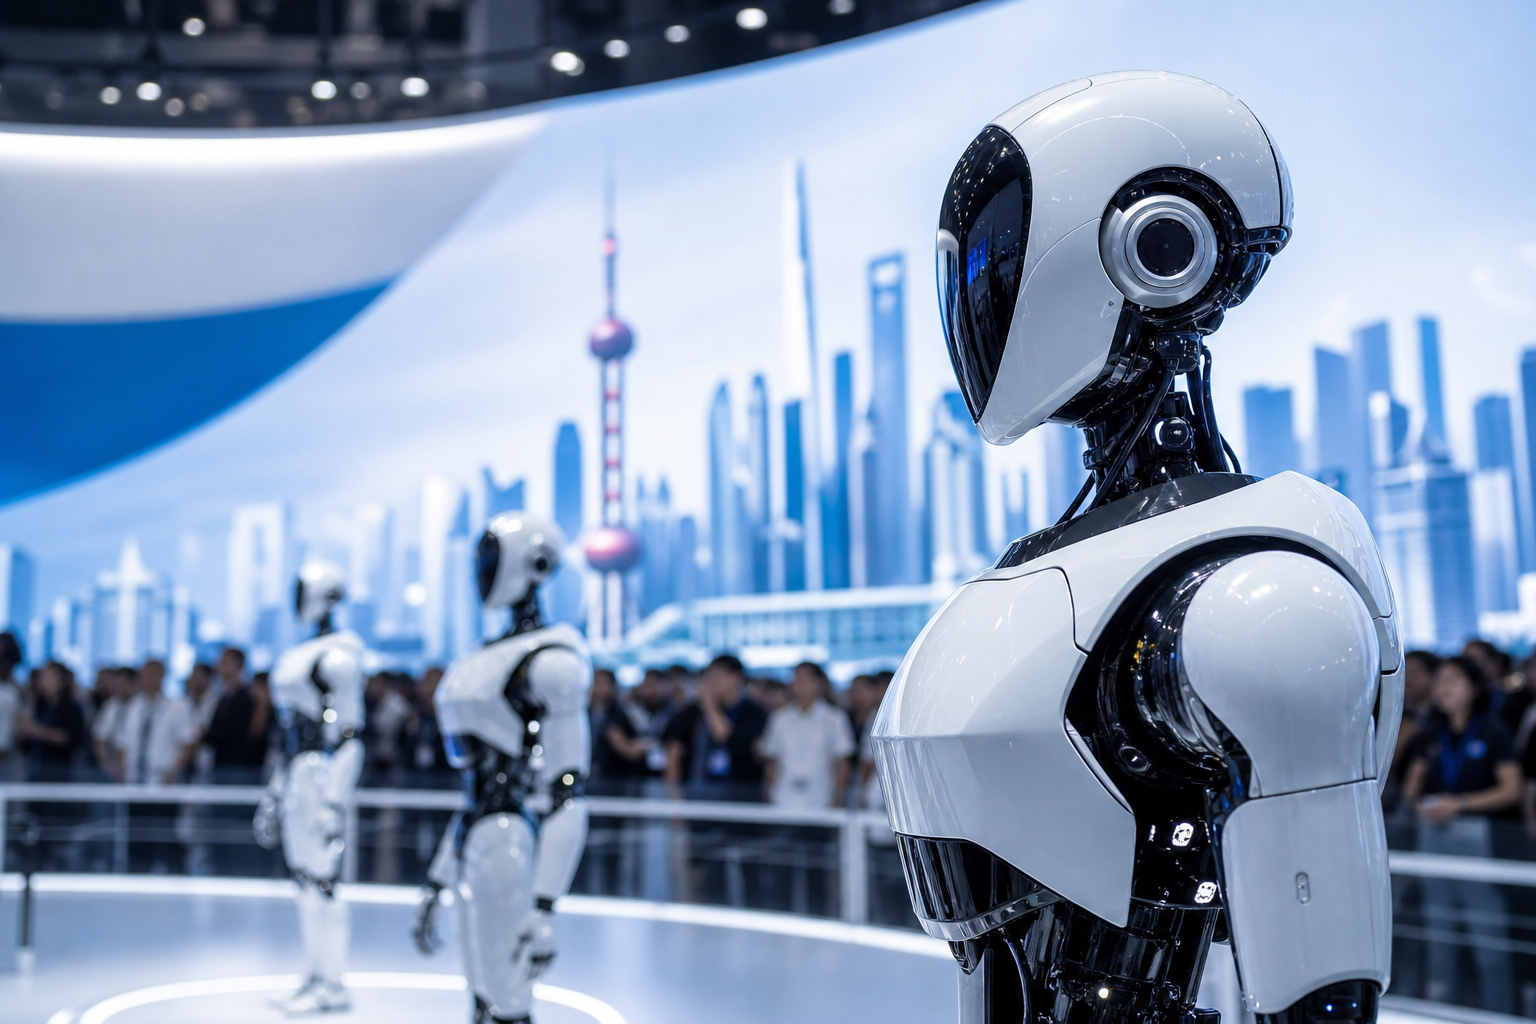 Highly Relevant
Why humanoid robots steal show at Shanghai AI event
Humanoid robots drew attention because they make AI tangible and testable in physical settings: movement, dexterity, safety, and autonomy are now as important as model performance. The Shanghai demos showed that hardware lets observers judge real-world behavior in ways slide decks and benchmarks cannot.
Read MoreReady to create amazing podcast content?
Choose a plan and start generating professional podcast content with AI
View Pricing Plans