OpenAI California AI regulation and SB 53 monitoring
OpenAI is urging California to make SB 53 focus on ongoing monitoring, reporting, and risk checks for advanced AI instead of one-time prelaunch promises. Under that approach, developers would need to document risks, retain evaluation and incident records, and demonstrate how safety controls work after deployment.
Key takeaways
- OpenAI frames the issue as requiring continuing evidence of safety because models change after release through fine-tuning, new tools, broader access, and evolving usage patterns.
- Monitoring rules in SB 53 would pull product, legal, trust and safety, security, and customer teams into the same chain of accountability.
- Operational changes from monitoring include updates to logging, incident response, regular evaluations, red-team procedures, access controls, and release approval workflows.
- California AI rules often influence procurement and vendor review outside the state because major AI companies build once and operate across many markets.
- Teams can prepare now by mapping model inventories, identifying high-risk use cases, defining reporting pathways, and setting documented thresholds for escalation before the final bill text is settled.
OpenAI California AI regulation and SB 53 monitoring
The reason this matters to you is simple. If you work in AI, policy, legal operations, product, or content strategy, you may soon need to explain what SB 53 asks for and what OpenAI is asking California to prioritize. The policy fight is not only about whether AI should be regulated. It is about how regulation should work when models change fast, model access spreads through APIs and open weights, and harms can emerge after release. A useful way to read OpenAI California AI regulation is as a debate over monitoring: what should be logged, who should report incidents, and when the state should step in. For a baseline risk framework that lawmakers and companies often reference, see the NIST AI Risk Management Framework.
What OpenAI California AI regulation is really arguing over
OpenAI California AI regulation is really arguing over whether California should require continuing evidence of safety, not just one-time promises made before a model launch. That distinction matters because advanced models do not stay static in practice. Providers fine-tune systems, add tools, broaden access, and connect models to business workflows that create new failure points after release.
If OpenAI is advocating for stronger monitoring in the SB 53 AI bill, the practical message is that regulators should be able to ask: what did you test, what are you watching now, what incidents have you seen, and what did you change after those incidents? Those questions are narrower and more operational than broad arguments about whether AI is good or bad. They fit the day-to-day reality of product governance.
For companies trying to interpret OpenAI California AI regulation, the takeaway is that compliance may become a living process. You may need recurring model evaluations, documented thresholds for escalation, and records showing how your team handles unsafe outputs or misuse attempts. This lines up with patterns already discussed in governance circles and with the risk-based approach outlined by NIST.
- Monitoring is different from static approval: A model can pass a release review and still create new risks later if usage changes, tools expand, or jailbreaking methods spread.
- SB 53 may shape process expectations: Even if your company is not directly named by California law, procurement teams and enterprise buyers may still ask whether your controls match the spirit of the bill.
- Risk evidence is likely to matter more than marketing claims: Internal records, eval results, and incident logs are easier for counsel and regulators to assess than broad public safety language.
This is also why content and communications teams should pay attention. If your company publishes AI claims or thought leadership, policy statements must match operational reality. A gap between messaging and monitoring will not hold up long. That is one reason governance-focused editorial planning on ContentPod has become more relevant for teams that need policy explanations grounded in actual workflows.
Why the SB 53 AI bill puts monitoring at the center
The SB 53 AI bill puts monitoring at the center because lawmakers need a way to govern systems that can create harm after deployment, not only during development. A law built around audits, disclosures, incident reporting, and safety checks gives regulators a tool that can adapt as models and use cases change.
That is the part of OpenAI California AI regulation that deserves the most attention. Monitoring rules are often less dramatic than model bans or licensing schemes, but they reach deeper into daily operations. If a provider must track certain categories of misuse, document serious safety incidents, or retain evaluation results, product, legal, trust and safety, security, and customer teams all get pulled into the same chain of accountability.
For readers who work in content or search, there is a parallel here. A policy regime based on observable evidence often produces better decisions than a regime based on claims. That same lesson appears in adjacent AI discussions, including AI safety testing results expose weak lab controls, where weak internal controls become visible only when testing is rigorous enough to surface them.
OpenAI California AI regulation also matters because California often acts as a policy laboratory for technology rules. Even when a bill applies only inside the state, vendors selling nationally may adopt one common operating model rather than maintain separate practices for California and everyone else. That can turn state law into a broader market standard.
If you are preparing for possible AI monitoring requirements, focus on concrete artifacts:
- Model inventory: A current list of models, major fine-tunes, tools, and deployment contexts.
- Evaluation records: Stored results for capability testing, misuse testing, and system-level safety checks.
- Incident definitions: A written standard for what triggers escalation, reporting, and review.
- Ownership map: Named teams and decision-makers for release approval, monitoring, and remediation.
Teams that already use structured publishing and governance workflows can adapt faster. The planning discipline described in seo workflows content consultants step by step plan is not written for legal compliance, but the same habit of documented review stages translates well to AI policy operations.
How OpenAI California AI regulation could affect product and compliance teams
OpenAI California AI regulation could affect product and compliance teams by turning AI safety from a periodic review task into an always-on operational function. That means more cross-functional work, more documentation, and more pressure to define what “adequate monitoring” means in measurable terms.
If you own an AI product, the first operational question is whether your current telemetry can tell you what regulators may ask. Can you identify high-risk prompts or outputs without storing unnecessary sensitive data? Can you separate harmless user experimentation from signs of misuse? Can you show when a model update changed behavior? These are not abstract questions. They determine whether California AI safety laws become manageable process work or a scramble after an inquiry arrives.
The second question is whether your governance model fits modern AI release cycles. Many teams still run approvals like a software change board from an earlier era. Advanced AI systems need closer feedback loops between evaluators, security, legal, and policy staff. That view also comes up in broader industry conversations such as The Future of AI in Business: From Hype to Reality, where the gap between AI messaging and operational readiness is a recurring theme.
When people discuss OpenAI regulatory stance, they often focus on whether a company wants more or less regulation. That framing misses the useful detail. A company may support stronger rules in one area, such as monitoring and reporting, while resisting vague or technically unworkable obligations elsewhere. The real policy work is in those distinctions.
For many organizations, the fastest path to readiness is a short internal gap review:
- List every model-related system: Include foundation models, wrappers, agents, fine-tunes, retrieval pipelines, and third-party APIs.
- Rank use cases by harm exposure: Customer service copilots, code generation, medical triage, financial recommendations, and content moderation do not carry the same risk profile.
- Check auditability: Confirm what is logged, how long logs are retained, and which teams can access them.
- Run a tabletop exercise: Simulate a harmful output incident and see whether reporting, remediation, and communication are clear.
If you publish AI-enabled content at scale, your monitoring discipline should also cover output quality and misuse vectors. The warning signs described in How AI generated religious books are flooding Amazon show what can happen when output volume rises faster than review standards.
Where OpenAI California AI regulation meets real implementation work
OpenAI California AI regulation meets real implementation work in logs, evaluations, access controls, and release gates. The policy language may sound legal, but the actual burden lands on teams that build, deploy, buy, or supervise AI systems.
The easiest mistake is to assume monitoring means only keeping records. In practice, good monitoring joins three separate tasks. First, you need visibility into model behavior. Second, you need a decision rule for when behavior becomes serious enough to escalate. Third, you need a response path that changes the system or the deployment conditions. Without all three, monitoring is just storage.
The table below shows how AI compliance rules may translate into concrete work streams.
| Policy concern | Operational question | Possible evidence |
|---|---|---|
| Misuse detection | Can the team identify suspicious prompt patterns or harmful tool use? | Alert thresholds, reviewer notes, access restrictions |
| Post-release safety | Does the model behave differently after updates or broader rollout? | Regression evals, canary tests, change logs |
| Incident reporting | What qualifies as a reportable event and who approves the report? | Incident taxonomy, response playbooks, timestamps |
| Third-party accountability | Can the company assess vendor models used inside products? | Vendor questionnaires, contract clauses, review records |
This is where OpenAI California AI regulation becomes relevant even for teams outside frontier model labs. Many businesses rely on third-party APIs and model providers. If California tightens monitoring expectations, buyers may ask vendors to prove their own safety process. The same pattern already appears in content operations. A brand that uses AI writing tools still owns the downstream output, which is one reason editorial controls discussed at ContentPod remain useful even outside policy-heavy industries.
- Example 1: A company offering an AI coding assistant may need stored eval results for prompt injection resilience and logging policies for misuse attempts tied to tools or repositories.
- Example 2: A healthcare workflow using a third-party model may need tighter human review triggers because incident response cannot rely only on the external vendor.
What good AI monitoring requirements look like in practice
Good AI monitoring requirements are specific enough to audit and flexible enough to adapt as systems change. That is the standard you should use when judging any version of OpenAI California AI regulation or the SB 53 AI bill.
Useful requirements usually answer five questions. What systems are covered? What risks must be tested? What counts as an incident? What records must be kept? When must a company report or remediate? If the law or policy cannot answer those questions, compliance turns into guesswork.
You can build toward that standard now. If your organization creates AI-generated marketing, support, research, or internal automation, the same discipline improves quality control and policy readiness at once. Workflows for prompt review, human approval, and output correction are not only editorial habits. They are early forms of governance. That is why teams discussing AI-assisted production often end up confronting similar oversight problems, as shown in ai-assisted content repurposing saas mistakes to avoid.
- Define model classes: Separate low-risk tools from systems used in sensitive contexts. A generic summarizer and an autonomous action-taking agent should not share the same review path.
- Tie monitoring to risk: High-risk deployments need deeper logging, eval frequency, and human review triggers than low-risk internal productivity tools.
- Write incident thresholds: Teams move faster when they know which events require containment, legal review, customer notice, or regulator contact.
If you need a workable starting point for governance language, ContentPod can help content and operations teams organize policy explanations, stakeholder updates, and structured editorial review around evolving California AI safety laws. The value is not hype. The value is having a documented process when standards tighten.
What to watch next in OpenAI California AI regulation
OpenAI California AI regulation is worth watching next for the details it may set on scope, documentation, and reporting triggers. The headline argument about stronger monitoring matters, but the compliance impact will depend on who is covered, what counts as a high-risk system, and how the state expects companies to prove they are doing the work.
The first challenge is overbreadth. A law that treats every AI deployment like a frontier model program may create noise and paperwork without improving safety. The second challenge is underdefinition. If monitoring duties are too vague, each company writes its own interpretation, and regulators get inconsistent evidence. The third challenge is vendor complexity. Many businesses deploy AI through outside providers, which means any workable rule must address shared responsibility.
These are the questions you should track when reading about OpenAI California AI regulation in 2026:
- Scope: Does SB 53 focus on advanced model developers, deployers in sensitive sectors, or both?
- Evidence: Are evals, incident logs, model cards, or external audits likely to be expected?
- Reporting: Does the law distinguish minor failures from serious reportable incidents?
- Interoperability: Can state rules map onto the NIST framework or other existing governance practices?
If you are building a response plan, keep one principle in mind. OpenAI California AI regulation is easier to manage when your team already knows where AI is used, who approves changes, and what evidence you can produce on demand. That is a business process issue as much as a legal one. Waiting for final enforcement action before building that process is usually the expensive option.
Conclusion: making the most of OpenAI California AI regulation
OpenAI California AI regulation is not only a news topic. It is a practical signal that California’s AI debate is moving toward monitoring, auditability, and post-release accountability. If OpenAI’s advocacy around SB 53 pushes lawmakers toward stronger oversight requirements, the companies that adapt fastest will be the ones that already treat model governance as ongoing operational work.
Your next step is to map your AI systems, define incident thresholds, and decide what evidence your team can produce if a customer, regulator, or executive asks how a model is monitored in production. If you need a place to organize policy content, internal explainers, and governance-focused editorial workflows, ContentPod can support that process without turning the work into a sales exercise. The main point of OpenAI California AI regulation is straightforward: stronger monitoring changes how AI teams document, review, and ship systems.
Bottom line: OpenAI California AI regulation matters because SB 53 may push AI safety law toward continuous monitoring, and companies that prepare documented oversight now will be in a better position than teams that rely on broad policy claims later.
Frequently Asked Questions
What is OpenAI California AI regulation?
OpenAI California AI regulation refers to the policy debate around how OpenAI wants California to regulate advanced AI systems, especially through stronger monitoring and oversight in SB 53. The phrase points to rules that may require developers or deployers to document risks, monitor model behavior, keep records, and respond to serious safety incidents.
What does the SB 53 AI bill appear to focus on?
The SB 53 AI bill appears to focus on oversight mechanisms that can track risk over time, rather than relying only on pre-release promises. That usually means attention to evaluation records, incident reporting, accountability for high-risk systems, and clearer expectations for how AI companies supervise models after deployment.
How should a business prepare for California AI safety laws in 2026?
A business should prepare for California AI safety laws in 2026 by creating a model inventory, ranking use cases by risk, documenting monitoring controls, and writing a clear incident response path. A business should also review vendor contracts, confirm what evidence can be produced on demand, and align internal governance with practical frameworks such as NIST so policy changes do not start from zero.
References & Further Reading
Share this post
You Might Also Like
Discover more content tailored to your interests
 Highly Relevant
Why anthropic model rivals fable on enterprise cost
Anthropic's model is being pitched as close enough in quality to a premium frontier model that cost-conscious enterprises may switch or diversify. The real test for buyers is whether the model delivers acceptable output on their highest-volume tasks while lowering total operating cost and governance overhead.
Read More Highly Relevant
How AI in sports marketing is changing broadcast ads
AI in sports marketing is enabling rights holders, networks, streaming platforms, and brands to sell more relevant inventory, adjust creative in real time, and tie ad performance to audience behavior across linear TV, streaming, social clips, and second-screen engagement. Those capabilities let teams coordinate campaigns across fragmented viewing paths and react to moment-level attention during live games.
Read More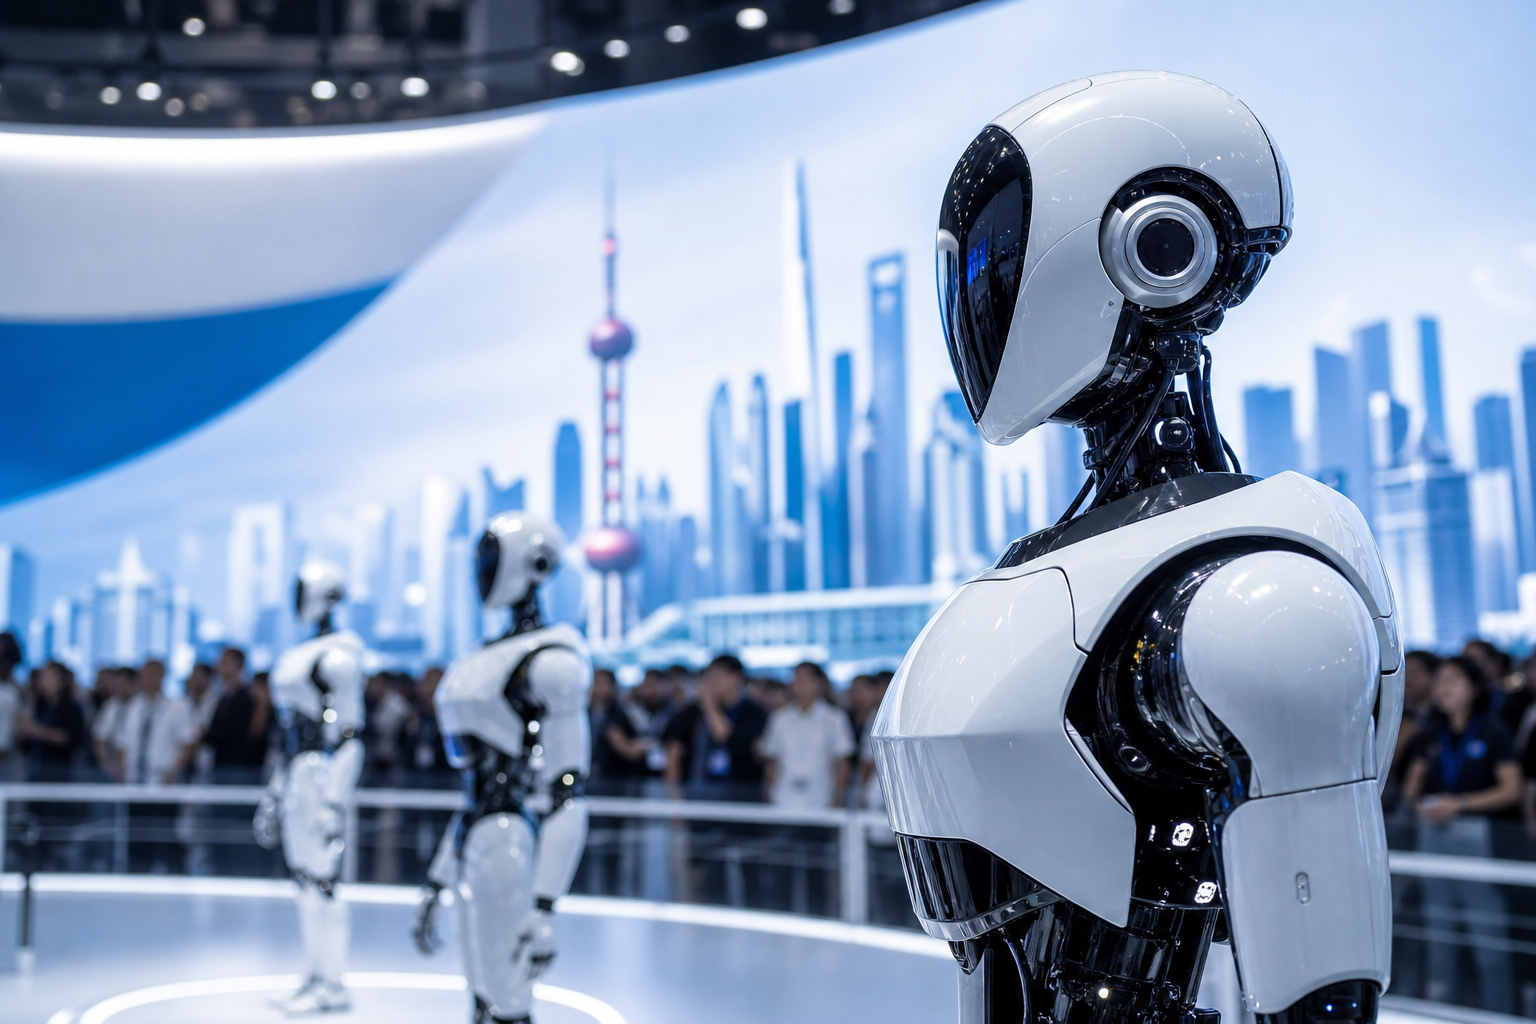 Highly Relevant
Why humanoid robots steal show at Shanghai AI event
Humanoid robots drew attention because they make AI tangible and testable in physical settings: movement, dexterity, safety, and autonomy are now as important as model performance. The Shanghai demos showed that hardware lets observers judge real-world behavior in ways slide decks and benchmarks cannot.
Read MoreReady to create amazing podcast content?
Choose a plan and start generating professional podcast content with AI
View Pricing Plans