Explained: Securing AI Systems: Experts Consider Research Priorities
Securing AI systems requires focused research and cross-sector collaboration to address technical, data, and operational risks. Experts at an April event recommended combining technical defenses, policy compliance, and operational practices to reduce those risks.
Key takeaways
- Core threats to AI systems identified by experts are adversarial attacks that manipulate inputs, risks to data privacy, and vulnerabilities within models.
- Priority research areas include methods to test AI systems against a variety of attacks, improving explainability to support human oversight, and ensuring compliance with existing and emerging regulations.
- Experts emphasized partnership across tech companies, security firms, universities, and government agencies to develop and deploy AI security solutions.
- Event case studies included a financial institution that prevented AI-driven fraud using stronger encryption, and a healthcare provider that experienced data breaches and then reassessed its security protocols.
- Practical best practices recommended are regular security audits, continuous real-time monitoring for threats, and employee training on security risks and protocols.
Explained: Securing AI Systems: Experts Consider Research Priorities
The rapid development of artificial intelligence (AI) systems has presented not only opportunities but also significant security challenges. With the increasing integration of AI into critical infrastructures, the need to prioritize securing these systems has become paramount. During an influential event in April, experts gathered to discuss the research priorities necessary for securing AI systems. In this article, we explore the key takeaways from this event, examining the considerations experts weigh when securing systems. For a deeper understanding of the implications of AI security, you can refer to NIST, which offers comprehensive resources on AI standards and security measures.
1. Identifying the Core Threats to AI Systems: Experts' Perspectives
When experts discuss securing systems, they often emphasize the necessity of understanding the core threats that AI systems face. These threats can range from data breaches to adversarial attacks that manipulate AI outputs. The April event highlighted several critical concerns that experts consider essential to address.
- Adversarial Attacks: These attacks involve manipulating input data to deceive AI models. Understanding the mechanisms and developing defenses against such attacks is crucial.
- Data Privacy: As AI systems process vast amounts of data, ensuring the privacy and integrity of this data is a top priority for experts. Techniques like differential privacy are often recommended.
- Model Vulnerabilities: Identifying and mitigating vulnerabilities within AI models themselves is essential. This includes regular audits and updates to AI systems.
For those interested in delving deeper into AI's impact on various sectors, consider reading Explained: If AI Owns the Decision, What Happens to Your Bank? on ContentPod.
2. Securing Systems Experts Consider: Research Priorities
The event also focused on delineating research priorities that can fortify AI systems against these threats. Experts agree that a multi-faceted approach is necessary, which includes both technological and policy-driven strategies. A few key research areas emerged as priorities.
- Robustness Testing: Developing methods to test AI systems against a variety of attacks to ensure robustness.
- Explainability: Enhancing the transparency of AI decisions to facilitate human oversight and trust.
- Regulation Compliance: Ensuring that AI systems comply with existing and emerging regulations to mitigate legal risks.
For a comprehensive guide on implementing SEO workflows in AI-driven environments, visit Mastering SEO Workflows for AI Content in B2B.
3. Collaborative Efforts in Securing Systems
Securing AI systems is not an isolated task; it requires collaboration across various sectors and disciplines. The April event underscored the importance of partnerships between academia, industry, and government agencies to address AI security challenges effectively.
- Cross-industry Partnerships: Encouraging joint ventures between tech companies and security firms to develop comprehensive security solutions.
- Academic Collaboration: Universities play a pivotal role in researching new security paradigms and training the next generation of experts.
- Government Initiatives: Government support in terms of funding and policy-making is crucial for fostering an environment conducive to research and development.
For insights into how AI is transforming business strategies, explore the AI and the Future of Content Marketing: A Dynamic Discussion interview on ContentPod.
4. Securing Systems Experts Consider: Case Studies
Real-world case studies offer invaluable lessons on the application of security measures in AI systems. During the event, several case studies were presented, highlighting successful and unsuccessful attempts to secure AI systems.
- Example 1: A financial institution that successfully thwarted AI-driven fraud through enhanced encryption methods.
- Example 2: A healthcare provider that implemented AI to streamline operations but faced challenges with data breaches, leading to a reassessment of their security protocols.
For more information on AI's expanding capabilities, check out Explained: Samsung Expands AI Capabilities of Bespoke AI Refrigerators with Family Hub.
5. Best Practices for Securing AI Systems
Experts outlined several best practices for securing AI systems, emphasizing the importance of proactive and holistic approaches. These practices are designed to help organizations safeguard their AI investments effectively.
- Regular Security Audits: Conducting frequent audits to identify and rectify vulnerabilities within AI systems.
- Continuous Monitoring: Implementing real-time monitoring solutions to detect and respond to security threats swiftly.
- Employee Training: Educating staff about potential security risks and protocols to enhance organizational security posture.
Consider exploring further strategies by visiting ContentPod for more insights on AI and technology.
6. Common Challenges and Mistakes in Securing AI Systems
Despite best efforts, organizations often face challenges and make mistakes when securing AI systems. Recognizing these pitfalls is essential for improving security measures.
- Over-reliance on Technology: Focusing solely on technology while neglecting human factors can lead to security oversights.
- Inadequate Testing: Failing to rigorously test AI systems under various scenarios can leave them vulnerable to attacks.
- Compliance Oversight: Not staying updated with regulatory changes can result in legal issues and security breaches.
For additional resources on AI security, consider visiting Anthropic, a leader in AI research and safety.
Conclusion: Making the Most of Securing Systems Experts Consider
Securing AI systems is a complex but necessary endeavor, requiring continuous effort and collaboration. By focusing on research priorities, embracing collaborative efforts, and adhering to best practices, organizations can significantly enhance their AI security posture. ContentPod offers valuable resources for those looking to stay ahead in AI security. Embracing the insights from the event on "securing systems experts consider" can be a transformative step for organizations seeking to protect their AI investments.
Frequently Asked Questions
What is securing systems experts consider?
Securing systems experts consider is the process of analyzing and implementing strategies to protect AI systems from various security threats, ensuring data privacy and model integrity.
Why is securing AI systems important?
Securing AI systems is crucial because these systems often handle sensitive data and perform critical functions. A breach can lead to significant financial and reputational damage.
How can organizations improve their AI security?
Organizations can enhance their AI security by conducting regular audits, implementing robust monitoring systems, and ensuring compliance with legal standards.
References & Further Reading
- April Event Highlights on AI Security
- OpenAI Research
- Anthropic: AI Safety
- NIST AI Standards
Share this post
You Might Also Like
Discover more content tailored to your interests
 Highly Relevant
Why anthropic model rivals fable on enterprise cost
Anthropic's model is being pitched as close enough in quality to a premium frontier model that cost-conscious enterprises may switch or diversify. The real test for buyers is whether the model delivers acceptable output on their highest-volume tasks while lowering total operating cost and governance overhead.
Read More Highly Relevant
How AI in sports marketing is changing broadcast ads
AI in sports marketing is enabling rights holders, networks, streaming platforms, and brands to sell more relevant inventory, adjust creative in real time, and tie ad performance to audience behavior across linear TV, streaming, social clips, and second-screen engagement. Those capabilities let teams coordinate campaigns across fragmented viewing paths and react to moment-level attention during live games.
Read More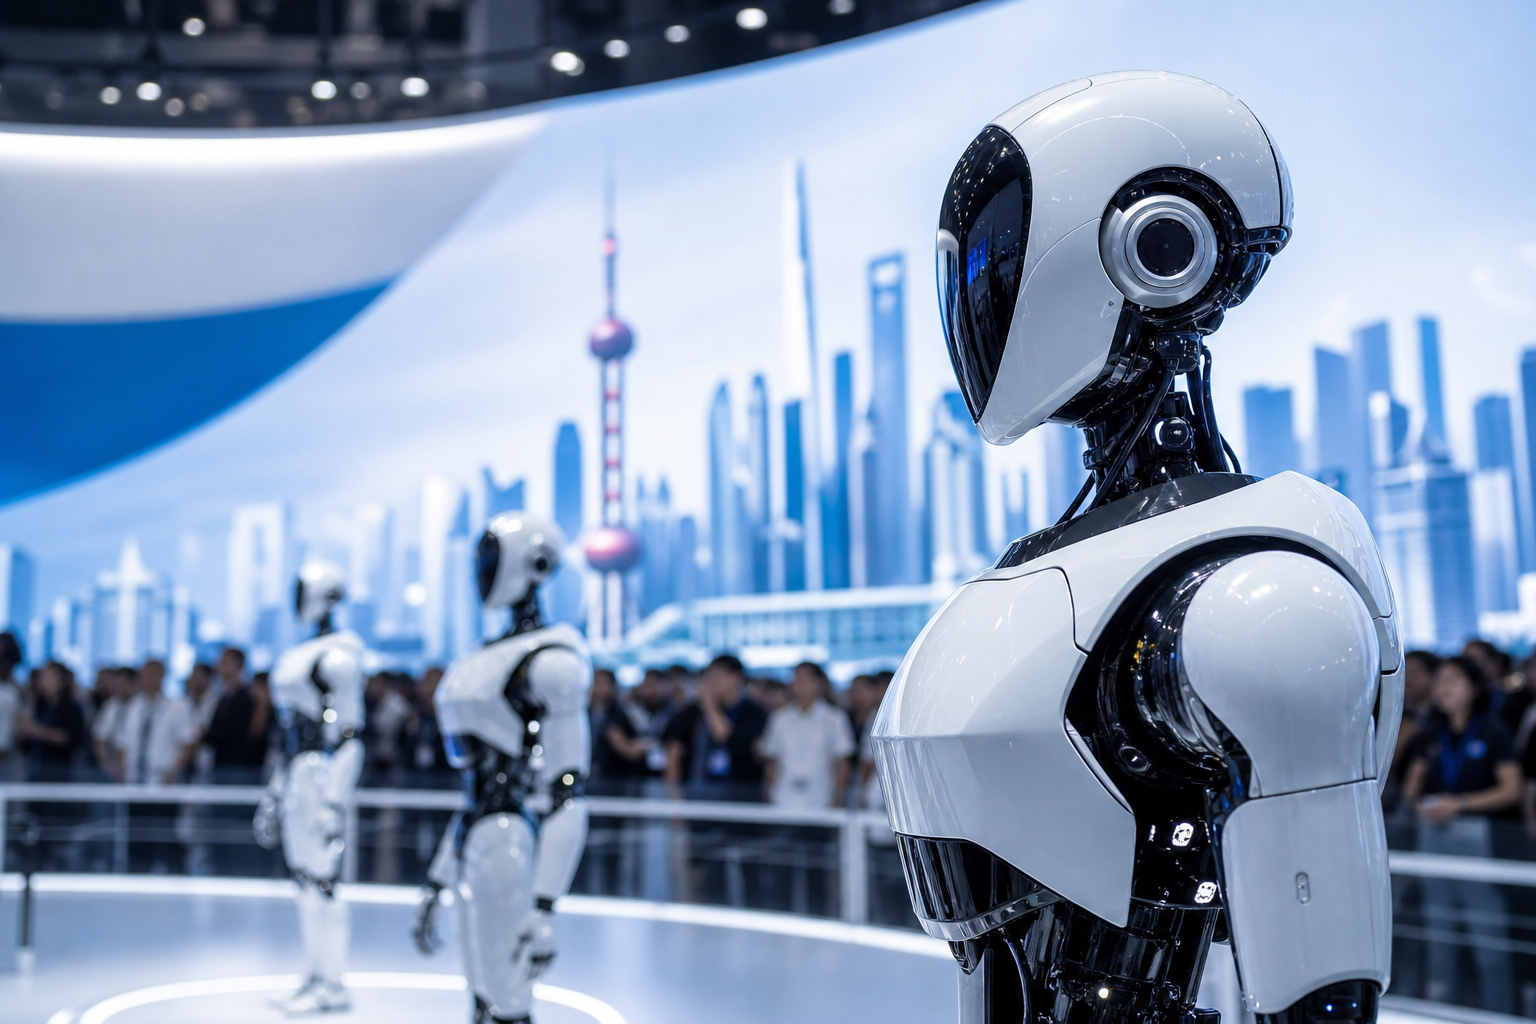 Highly Relevant
Why humanoid robots steal show at Shanghai AI event
Humanoid robots drew attention because they make AI tangible and testable in physical settings: movement, dexterity, safety, and autonomy are now as important as model performance. The Shanghai demos showed that hardware lets observers judge real-world behavior in ways slide decks and benchmarks cannot.
Read MoreReady to create amazing podcast content?
Choose a plan and start generating professional podcast content with AI
View Pricing Plans